What if the most dangerous DeFi mistake is not choosing the wrong protocol, but approving a transaction whose consequences you never truly saw? In a US wallet, the security problem is broader than holding an asset safely. You must understand what your portfolio contains, what a transaction is attempting to change, and how public transaction ordering can affect the result. Portfolio tracking, transaction simulation, and MEV protection address different parts of that problem. Treating them as interchangeable creates false confidence; combining them creates a more useful risk-management system.
That distinction matters because wallet security is not a single feature. A portfolio view helps with awareness. Simulation helps with interpretation before signing. MEV-aware execution helps reduce certain risks after a transaction is submitted. Each operates at a different stage, and each has failure modes. An advanced EVM wallet such as rabby wallet is most useful when its features are treated as instruments for verification rather than as substitutes for judgment.
Portfolio tracking is the first line of defense, not an accounting extra
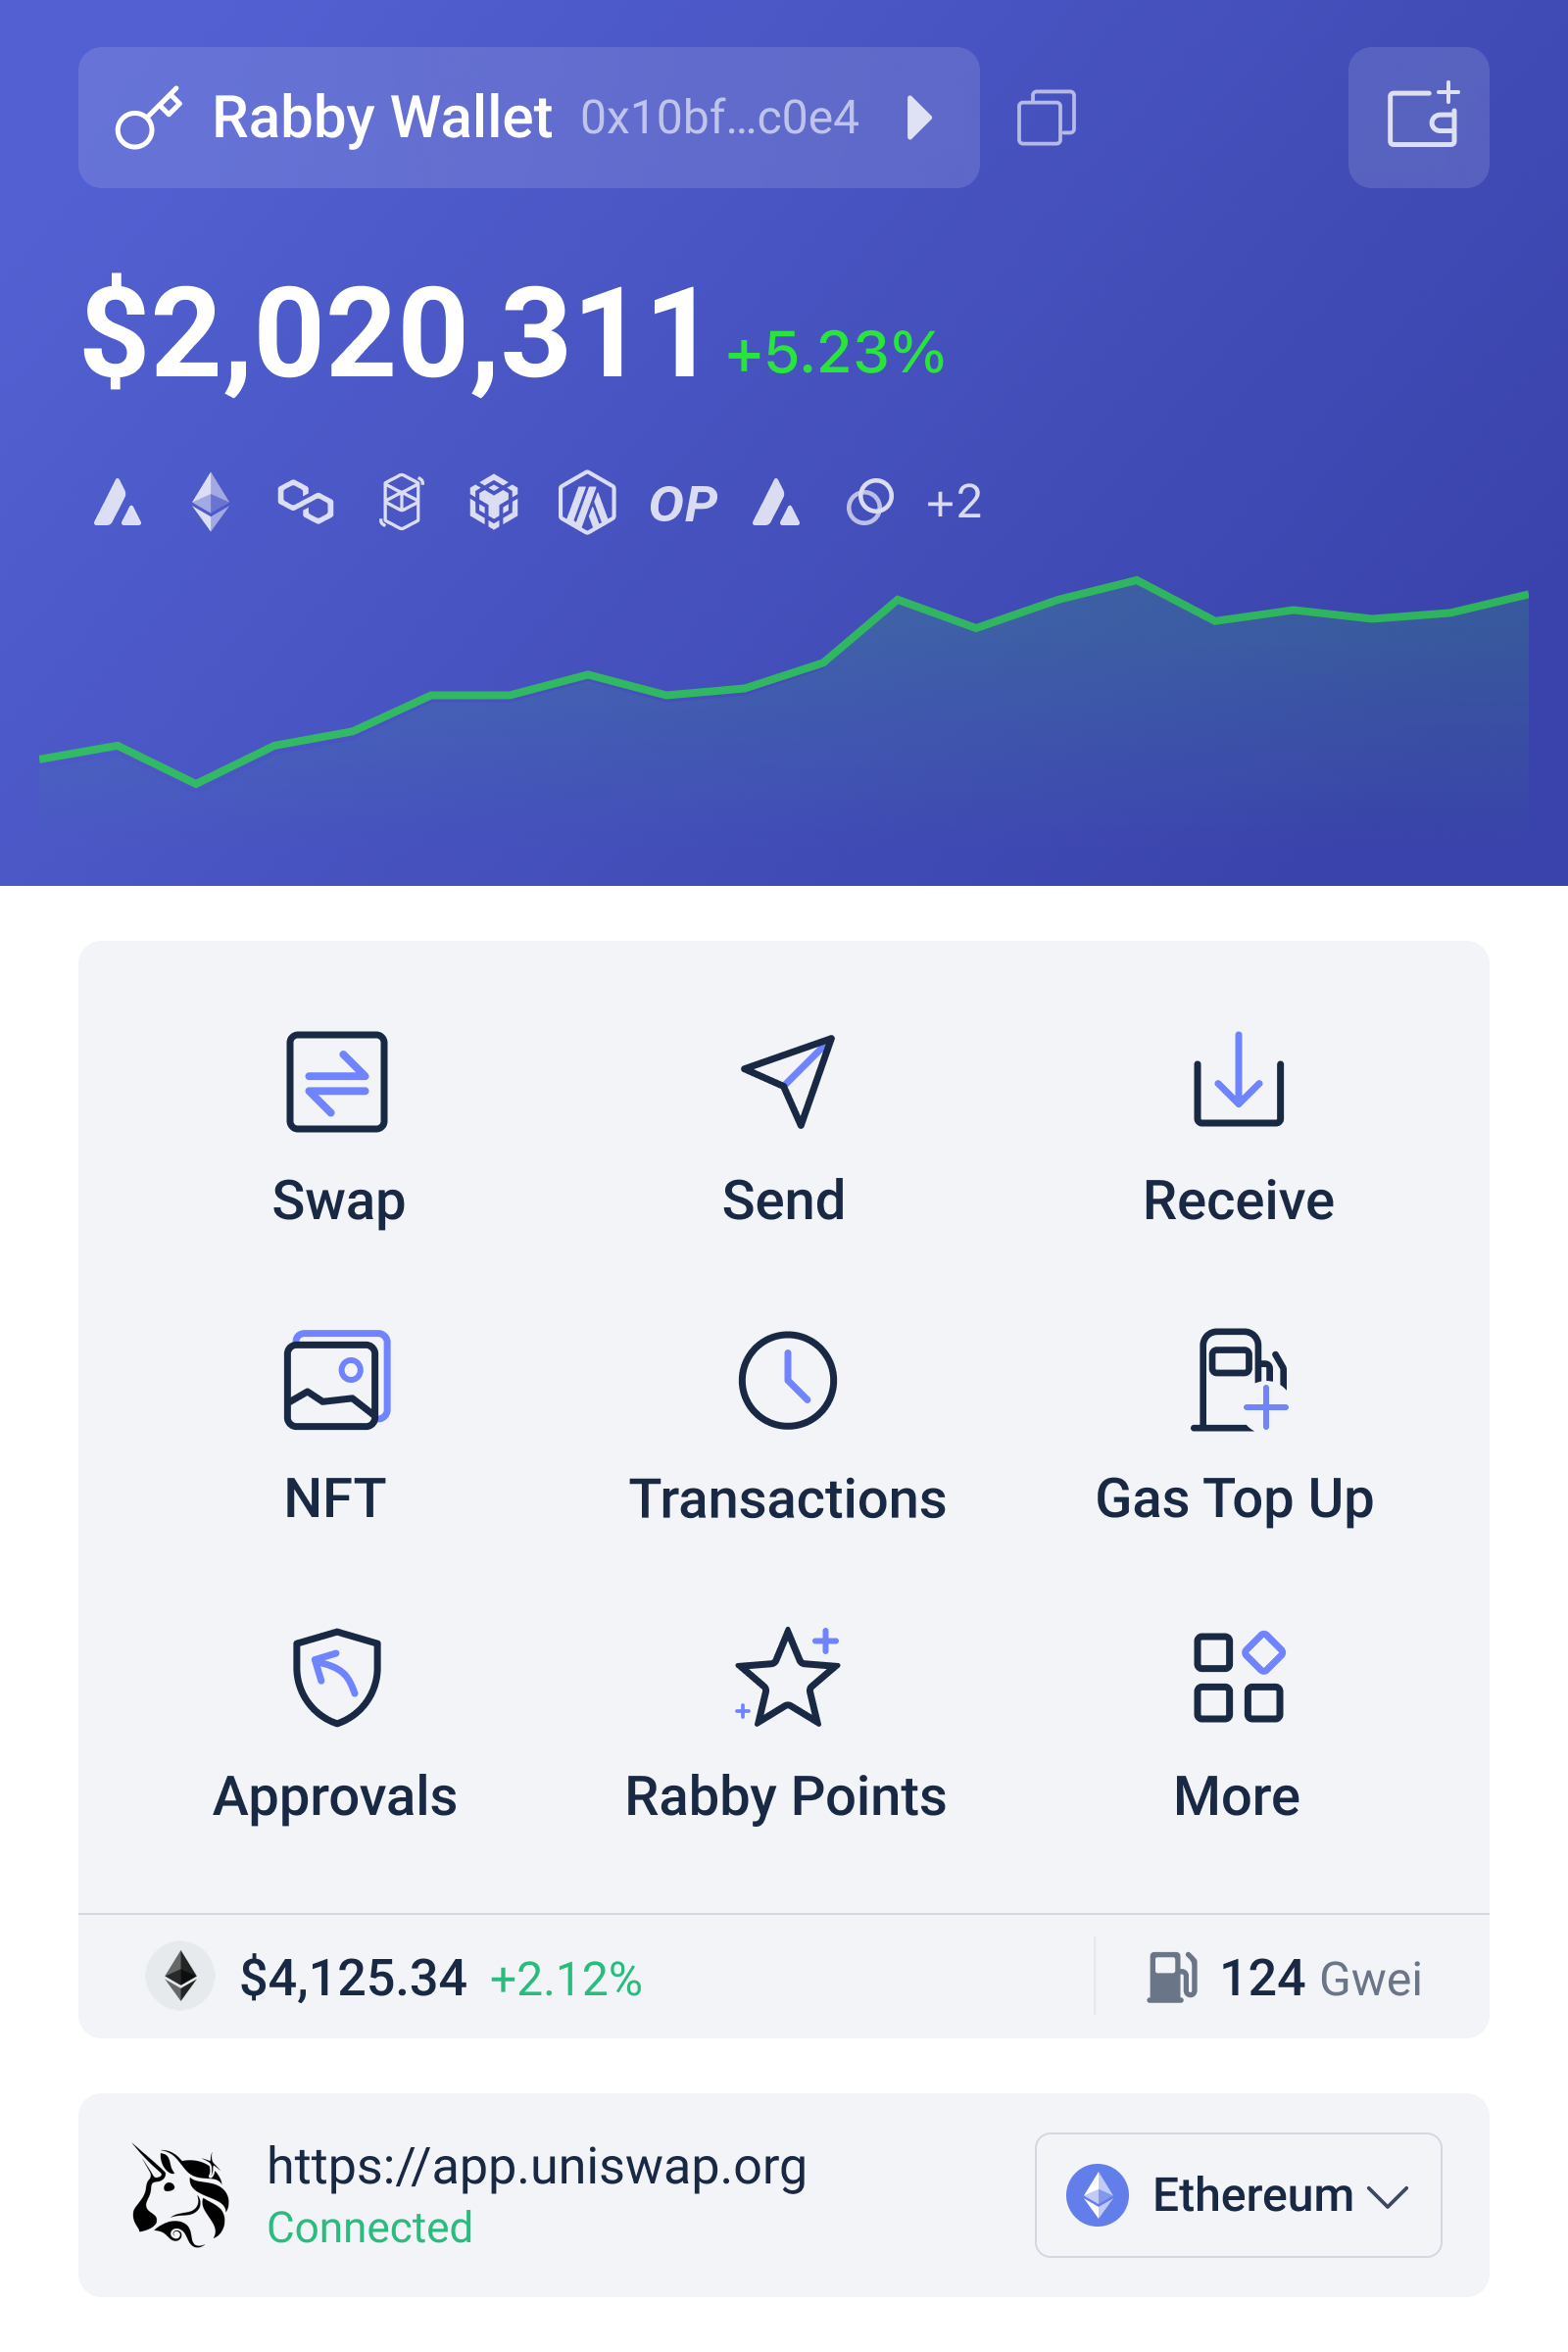
Portfolio tracking sounds passive, but it can reveal active security problems. A useful tracker aggregates wallet balances, tokens, positions, and activity across supported Ethereum-compatible networks. That gives a user a baseline: which addresses are controlled, which assets should exist, and which changes require explanation.
The non-obvious point is that a portfolio is not simply a list of token balances. It is a collection of permissions, claims, and dependencies. A wallet may hold a liquid token, a staked position, a liquidity-provider receipt, a lending claim, or an obscure token created by an unsolicited airdrop. Two assets with similar dollar values can have very different risks because one may depend on a protocol’s solvency while the other is immediately transferable.
Tracking also helps identify operational drift. An unfamiliar approval, a new spending permission, or a balance that changes without a clearly remembered action can be an early warning signal. Yet portfolio tracking has limits. Price data can be delayed or unavailable, illiquid tokens may display misleading valuations, and a dashboard cannot independently prove that a protocol is solvent or that a token contract is safe. Visibility is not verification.
Transaction simulation translates intent into consequences
Signing a transaction is often described as authorizing an action, but the wallet interface may show only technical fields: a contract address, a method name, and an amount. Simulation adds a more practical layer by estimating how the wallet’s state could change if the transaction were executed. Depending on the network and integration, that may include token transfers, approvals, swaps, contract interactions, and changes in balances.
This is valuable because the human-readable label on a website is not the same thing as the contract call submitted to a blockchain. A button that says “deposit” may involve a token approval followed by a deposit. A swap may route through several contracts. A malicious or compromised front end could request an unexpected transfer while presenting familiar language in the browser.
Simulation therefore works as a pre-signing question: “What does this transaction appear likely to do?” That is stronger than blindly trusting the dapp, but weaker than a guarantee. Simulations can diverge from final execution when state changes between the simulation and inclusion, when a contract behaves differently under changing conditions, or when the simulator cannot fully interpret a custom call. Reverted simulations are important warnings, but successful simulations do not certify a contract’s intentions.
For practical review, focus on the delta rather than the transaction’s technical vocabulary. Which assets leave the wallet? Which assets arrive? Is a new approval being granted, and is its allowance larger than necessary? Does the resulting position match the economic purpose of the action? If a transaction claims to mint, bridge, or stake but simulation shows an unrelated transfer, stop. That mismatch is more informative than a polished website.
MEV protection addresses a different threat
Maximum extractable value, commonly called MEV, refers to value that can be gained by influencing or reacting to transaction ordering. In a public mempool, pending transactions may be visible before confirmation. Searchers and other participants can sometimes use that information to place transactions around a user’s trade, capture arbitrage, or exploit predictable execution conditions.
MEV protection is therefore not mainly about whether a user is interacting with a malicious contract. It concerns how a legitimate transaction may be executed in a competitive ordering environment. A large swap with high price impact, for example, can become attractive to an external actor even when the user selected a reputable protocol.
Protection mechanisms vary. A wallet or service may route transactions through private submission channels, use specialized RPC infrastructure, or apply execution settings intended to reduce public exposure. These approaches can reduce some forms of front-running or sandwich activity, but they introduce trade-offs. Private routing may depend on an intermediary, may not be available on every chain, and does not eliminate smart-contract risk. It can also alter inclusion behavior: a transaction hidden from the public mempool might be less broadly propagated if the chosen route fails.
There is another boundary worth emphasizing. MEV protection cannot rescue an economically bad trade. If slippage tolerance is set too high, a private route does not make the price fair. If a user approves unlimited spending to a compromised contract, concealment from searchers does not solve the approval risk. MEV controls protect the path to execution; they do not validate the destination.
A side-by-side framework for choosing the right control
Portfolio tracking is strongest after activity has occurred: it helps users notice what they own and whether the wallet’s state remains plausible. Transaction simulation is strongest immediately before signing: it tests whether the proposed state change resembles the user’s intent. MEV protection is strongest during submission and ordering: it seeks to reduce information leakage or adverse sequencing.
That means the tools are complementary rather than competing. A user who relies only on tracking may detect a problem late. A user who relies only on simulation may approve a transaction that is accurately simulated but economically unfavorable. A user who relies only on MEV protection may still interact with a dangerous contract. The safer workflow is sequential: establish a portfolio baseline, inspect the proposed state change, then choose an execution path appropriate to the transaction’s size and sensitivity.
For routine transfers to a known address, elaborate MEV controls may add little value, while address verification remains critical. For a volatile token swap, simulation and slippage review deserve priority, with MEV-aware routing potentially useful. For lending, staking, or liquidity transactions, the central questions extend beyond execution: what permissions are granted, what risks are inherited, and how difficult is it to unwind the position?
The main misconception: a warning is not a verdict
Security interfaces often display warnings, risk labels, or simulations in a way that users may interpret as a binary approval system. That is dangerous. A clean result means the available analysis did not identify a particular problem under the conditions tested. It does not mean the protocol is reputable, the token will retain value, or the transaction cannot be exploited later.
Conversely, an unfamiliar contract or incomplete simulation is not automatic proof of fraud. New protocols, custom contracts, and unusual transaction types may simply exceed the tool’s interpretive coverage. The correct response is not to ignore every warning or obey every warning blindly. It is to reduce exposure: use a smaller test amount, verify the contract address through an independent channel, revoke unnecessary permissions, and avoid signing when the economic outcome cannot be explained.
This is where custody and convenience meet. A self-custody wallet preserves user control, but it also leaves the user responsible for seed security, device hygiene, phishing resistance, and transaction interpretation. A feature-rich wallet can reduce cognitive load, yet the final authorization remains a high-consequence decision. The interface should make careful behavior easier; it cannot make responsibility disappear.
A practical risk-management routine for DeFi users
Before signing, identify the intended outcome in plain language. “Exchange a defined amount of one token for another within a defined price range” is useful. “Click the button on a familiar site” is not. Compare that intention with the simulation’s asset movements and permissions.
Next, separate approval from action. An approval grants a contract permission to spend a token later; it is not the same as completing the intended swap, deposit, or stake. Check whether the allowance is limited and whether an old approval is still necessary. Periodic review of approvals is particularly important for wallets used across many dapps.
Then consider execution conditions. Review slippage, gas, network selection, recipient address, and whether the transaction is likely to be exposed in a public mempool. MEV protection may be most relevant for larger or price-sensitive trades, but its availability and effectiveness are chain- and route-dependent.
Finally, compare the post-transaction portfolio with the expected result. If the position, balance, or approval state differs from what was predicted, investigate before continuing. This closes the loop between tracking, simulation, and execution. The process resembles a small control system: observe the current state, model the proposed change, execute cautiously, and measure the outcome.
What to watch next
The likely direction of wallet security is greater integration between portfolio intelligence, transaction interpretation, and execution choice. If these layers become more tightly connected, a wallet could present not just “sign” or “reject,” but a contextual risk picture: the assets affected, the permissions created, the estimated economic exposure, and the likely execution path.
That development would be useful, but it raises a new question: who defines acceptable risk? Automated systems may be good at detecting unusual state changes while remaining poor at understanding a user’s broader strategy. DeFi users should therefore watch whether tools expose their assumptions and uncertainty, not merely whether they produce confident-looking labels. Transparency about what was simulated, what was not, and which execution route is being used will matter as much as additional automation.
FAQ
Does transaction simulation guarantee that a DeFi transaction is safe?
No. Simulation estimates the likely result under particular blockchain conditions. It can reveal unexpected transfers, approvals, or reverts, but it cannot guarantee that a contract is trustworthy, that prices will remain favorable, or that state will not change before inclusion.
Is MEV protection necessary for every transaction?
No. Its value depends on the transaction, chain, route, size, and market conditions. It may be especially relevant for large or price-sensitive swaps, while address verification and approval review may matter more for a simple transfer or contract interaction.
Why does portfolio tracking matter if I already check each transaction?
Transaction review is forward-looking; portfolio tracking is state-based. Tracking helps reveal unexplained approvals, unexpected balances, and changes that may only become obvious after execution. The two views catch different classes of error.
The strongest mental model is simple: tracking tells you where you are, simulation estimates where a transaction may take you, and MEV protection concerns how the journey is exposed to the market. None is a magic shield. Used together, however, they turn wallet security from a single moment of clicking “confirm” into a repeatable process of observation, verification, and controlled execution.